Cyber threats are becoming more sophisticated, and business leaders need a clear understanding of the risks facing their organisations.
Join cybersecurity specialists from Sentrian and Division 5 for an interactive session designed for business owners, executives, managers, and other non-technical decision-makers. You'll gain practical insights into today's cyber threat landscape, understand how AI is changing the risk environment, and learn how to assess your organisation's cybersecurity readiness.
Attendees will leave with a better understanding of the threats that matter most, and practical actions they can take to strengthen security, reduce risk, and improve business resilience.

Thursday, October 22, 2026

2 - 3 pm

Online via Microsoft Teams

Free
What we'll cover
01
02
03
04
05
06
This webinar is designed for business leaders and professionals responsible for protecting their organisation, people, and data, including:

Business leaders, owners, directors, executives, and managers responsible for organisational resilience and operations.
IT leaders, Microsoft 365 administrators, and professionals overseeing technology, cybersecurity, risk, compliance, governance, and privacy.
Decision-makers involved in cybersecurity, business continuity, or technology strategy, particularly in legal, financial services, healthcare, not-for-profit, property, and construction sectors handling sensitive information.
Growing teams that need AI to work within the systems they already run
Where client work, deadlines, and documentation drive the day
Including government, legal, medical, accounting, property, infrastructure, and construction
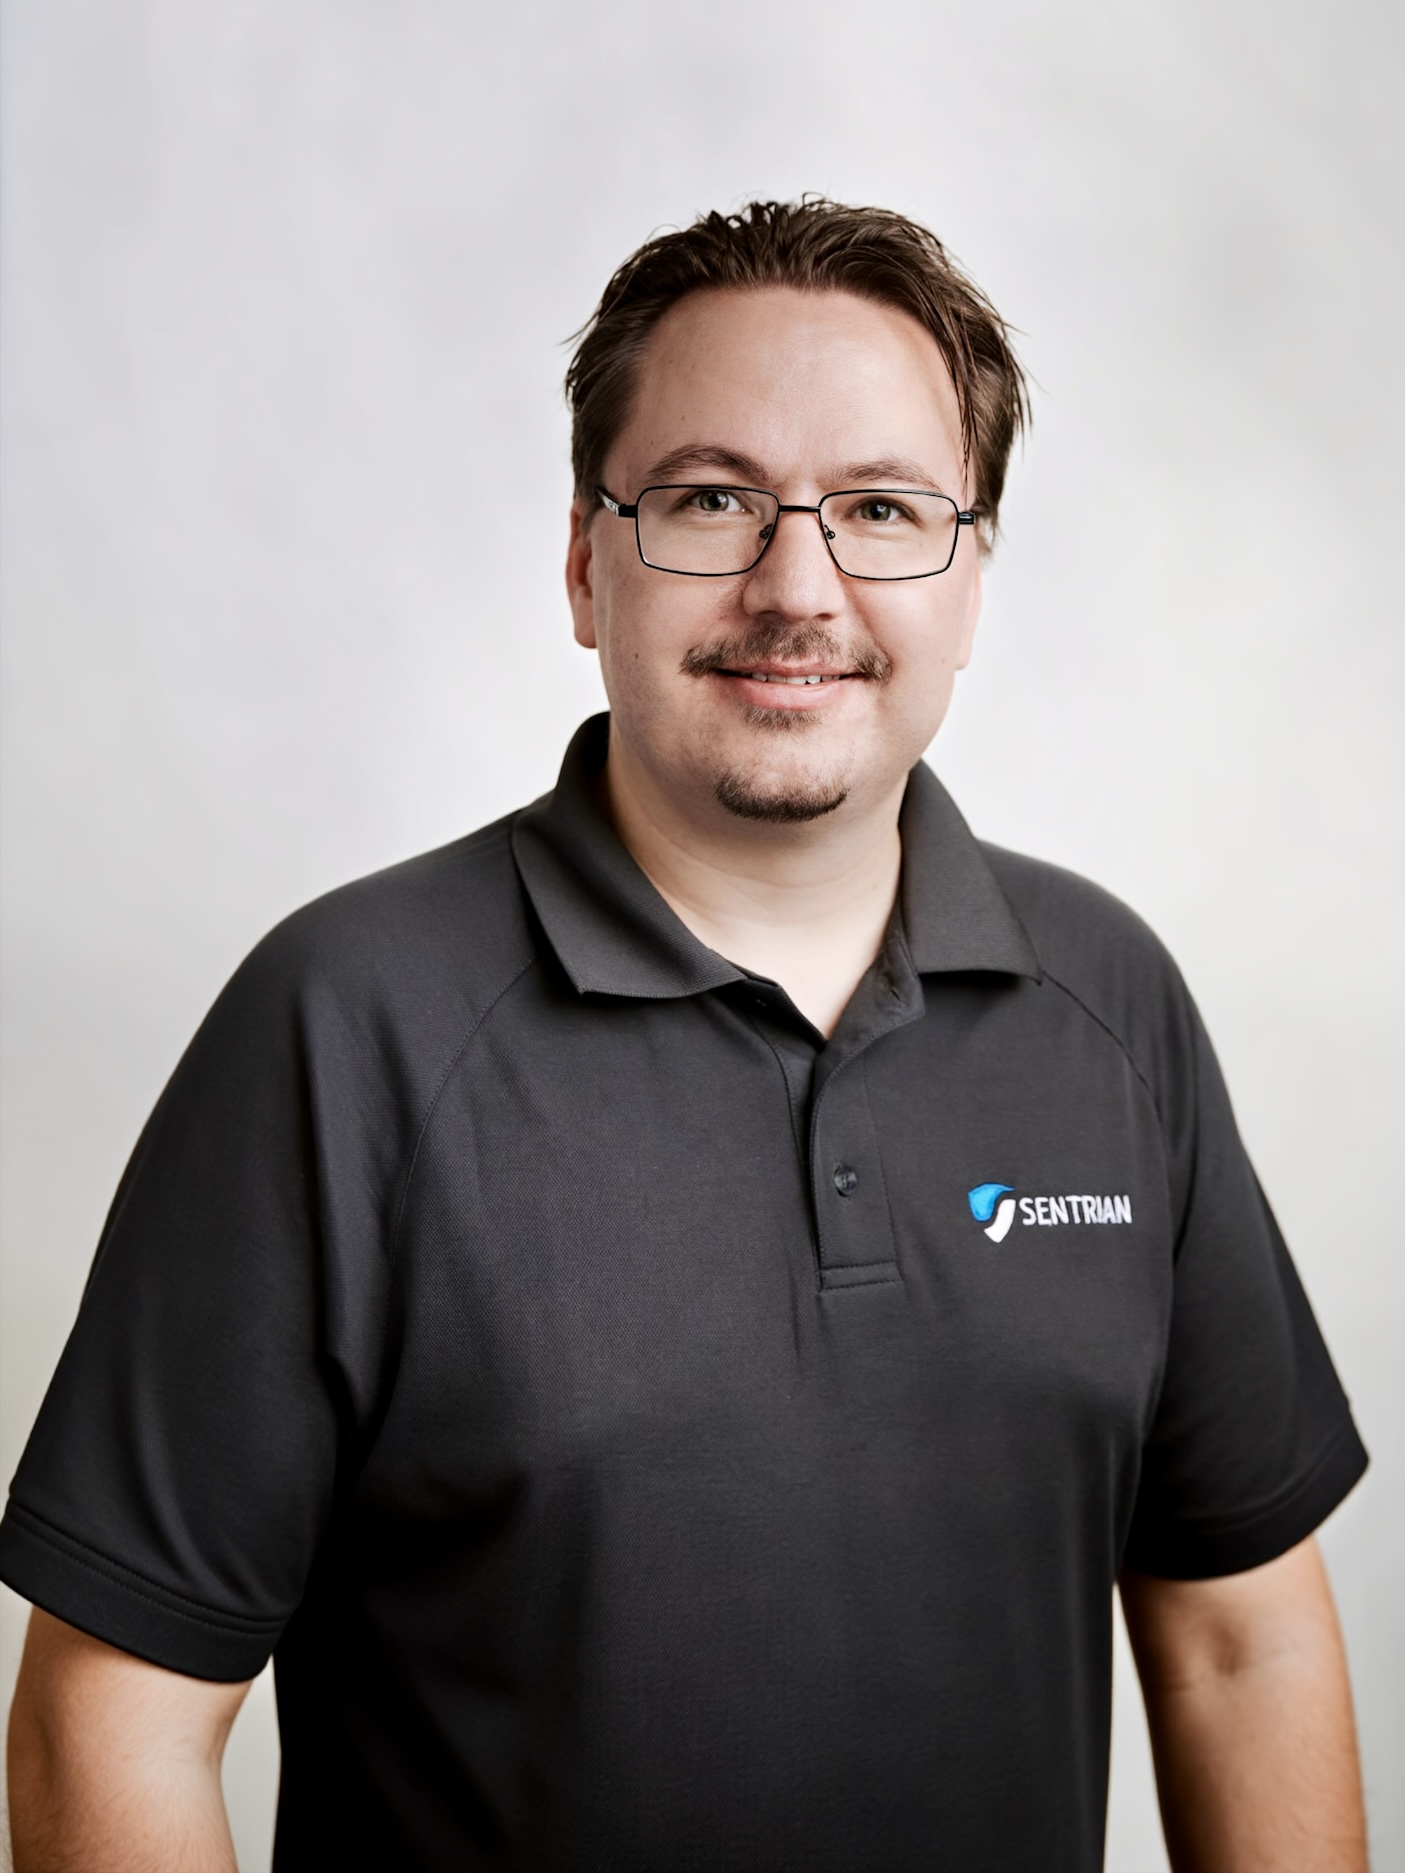
Alex is a Senior Systems and Security Engineer at Sentrian. He helps organisations strengthen their security posture through identity and endpoint security, automation, and modern Microsoft technologies.
Alex specialises in Active Directory, Microsoft Entra ID, Intune, Defender, and Sentinel. He works with organisations across Australia to implement security controls, improve cyber resilience, and automate operational processes. Alex also delivers cybersecurity training and awareness programs, helping teams understand emerging threats and adopt security best practices.
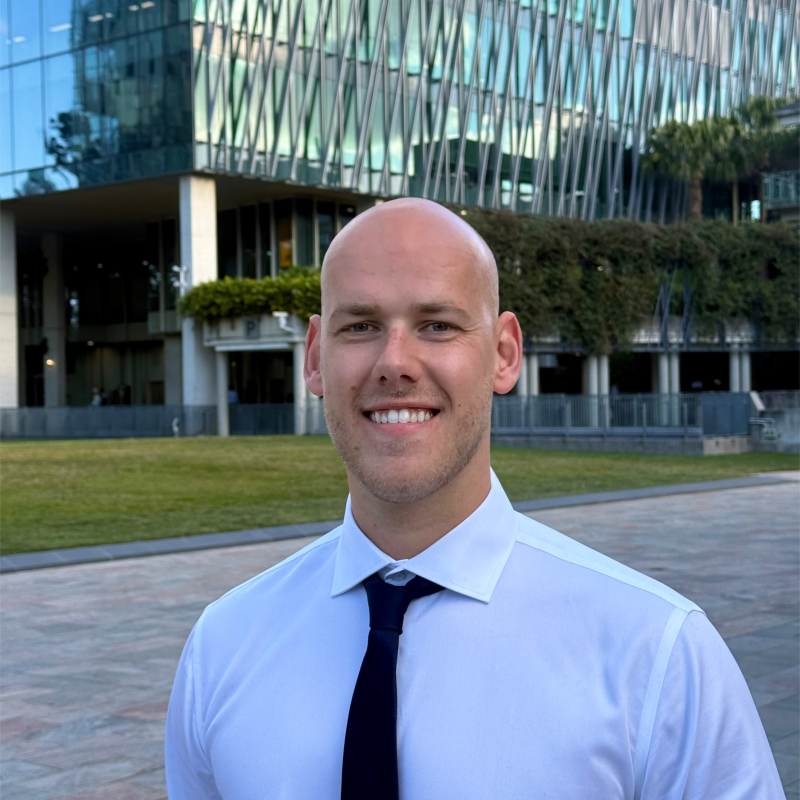
Koen is a Governance, Risk and Compliance (GRC) Specialist at Division 5's Strategy team, bringing a strong foundation in data analysis, governance and compliance frameworks. He takes an analytical approach to security engagements, helping clients understand and manage their cyber risk and turn complex information into practical outcomes.
His work includes threat and risk assessments, third-party security program design, and compliance analysis, including helping organisations align with common frameworks. Koen's background in business intelligence allows him to make risk measurable and visible, developing clear metrics, reporting structures and documentation that support decision-making and strengthen governance.
Koen is a certified ISO 27001:2022 Lead Auditor and holds a Bachelor of Business Engineering from the Amsterdam University of Applied Sciences and a Master of Information Technology (Cyber Security) from QUT.